Recent Education Sector Cyber Attacks

Page 3 of 6
China-Nexus Spearphish Fakes Gmail Attachments

China-Nexus Spearphish Fakes Gmail Attachments

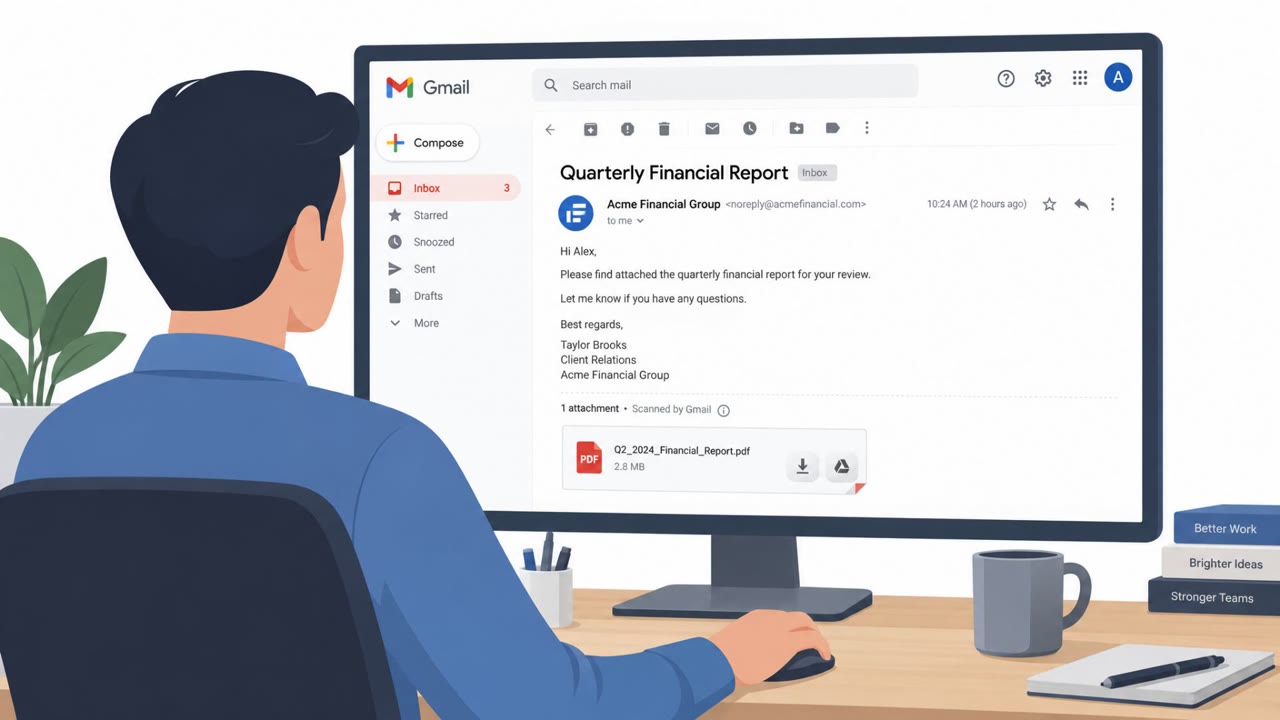
Cisco Talos reports a China-nexus cluster (UAT-11587) using targeted spear‑phishing against government and policy organizations across Asia. The attackers spoof trusted senders and use an email that visually clones Gmail’s attachment preview to trick recipients into clicking a Cloudflare-hosted…

September 30, 2026
Star Blizzard’s RedFlick Phish Uses VHDX Trap

Star Blizzard’s RedFlick Phish Uses VHDX Trap

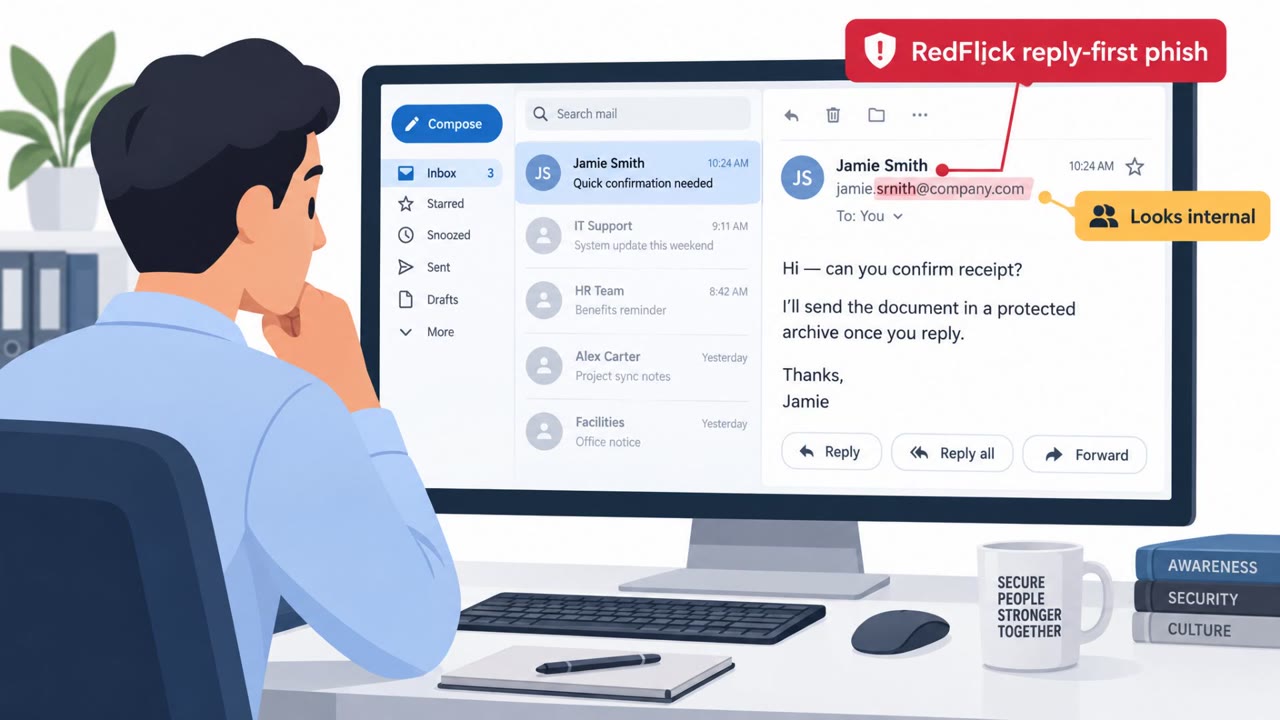
Microsoft reports real-world Star Blizzard phishing campaigns where victims who engage with an initial email receive a follow-up message containing a password-protected ZIP/RAR attachment. The attachment chain hides a malicious shortcut disguised as a PDF, opening a decoy file while quietly…

September 30, 2026
Star Blizzard Scales Phishing With “RedFlick”

Star Blizzard Scales Phishing With “RedFlick”

Microsoft reports that the Russian state-linked actor Star Blizzard ran large-scale phishing campaigns in 2026 that use convincing lures like tax notices, fines, and “closed-door” event invitations. After a victim replies, the attacker sends a password-protected ZIP/RAR attachment that triggers a…

September 29, 2026
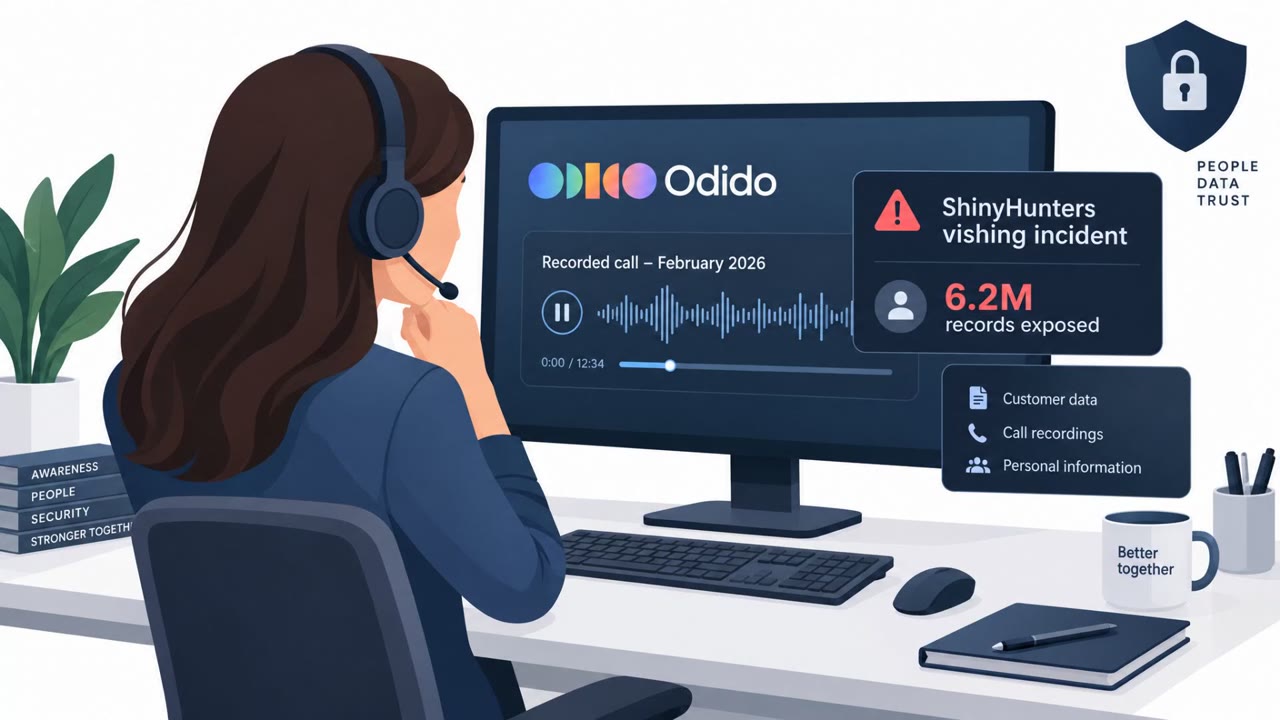
ShinyHunters Talked Into Odido via Spoofed Login

ShinyHunters Talked Into Odido via Spoofed Login

Dutch police are investigating ShinyHunters after a phone-based social engineering incident helped attackers break into Odido, the Netherlands’ largest mobile provider. Investigators say the caller persuaded an employee to log into a spoofed website, which was then used to steal data on more than…

September 28, 2026
EvilTokens Used Device-Code Phish to Fuel BEC

EvilTokens Used Device-Code Phish to Fuel BEC

Microsoft disrupted “EvilTokens,” a subscription cybercrime service that stole Microsoft account access using device-code phishing and then used AI-style automation to rapidly mine victims’ inboxes for payment and org-chart details. The goal was to quickly craft believable payment-fraud messages…

September 23, 2026
Microsoft Disrupts ‘EvilTokens’ Phishing Service

Microsoft Disrupts ‘EvilTokens’ Phishing Service

Microsoft says it disrupted the “EvilTokens” phishing-as-a-service platform, which it links to compromises of over 12,000 inboxes across more than 10,000 organizations. The service used AI to tailor phishing emails to a victim’s role and to analyze compromised inboxes to identify trusted…

September 23, 2026
EvilTokens MFA Phish Hijacked 12,000 Inboxes

EvilTokens MFA Phish Hijacked 12,000 Inboxes

Microsoft and partners disrupted “EvilTokens,” a phishing service that helped criminals break into more than 12,000 mailboxes across 10,000+ organizations. Victims were tricked into entering an authentication code on a real Microsoft sign-in page, letting attackers capture access tokens and get…

September 23, 2026
EvilTokens Used Device-Code Phish + AI for BEC

EvilTokens Used Device-Code Phish + AI for BEC

Microsoft disrupted EvilTokens, a phishing-as-a-service operation linked to thousands of compromised Microsoft 365 inboxes. The group used “device code” phishing to steal valid session tokens (not passwords) and then used an AI chatbot to scan mailboxes and help craft business email compromise…

September 22, 2026
China-Linked Phish Uses Fake Sites to Exploit Chrome

China-Linked Phish Uses Fake Sites to Exploit Chrome

Researchers say a China-aligned group (UTA0565) sent phishing emails to government targets and used multiple fake websites to lure victims into visiting pages that triggered a Chrome-and-Windows zero-day exploit chain. The messages used political advocacy themes and spoofed well-known organizations…

September 22, 2026
Device-Code Phishing Service Hit After 12K Breaches

Device-Code Phishing Service Hit After 12K Breaches

Microsoft and partners disrupted “EvilTokens,” a phishing-as-a-service platform Microsoft links to over 12,000 compromised inboxes across more than 10,000 organizations. The service used deceptive emails to trick people into pasting a “device code” into Microsoft’s real sign-in page…

September 22, 2026
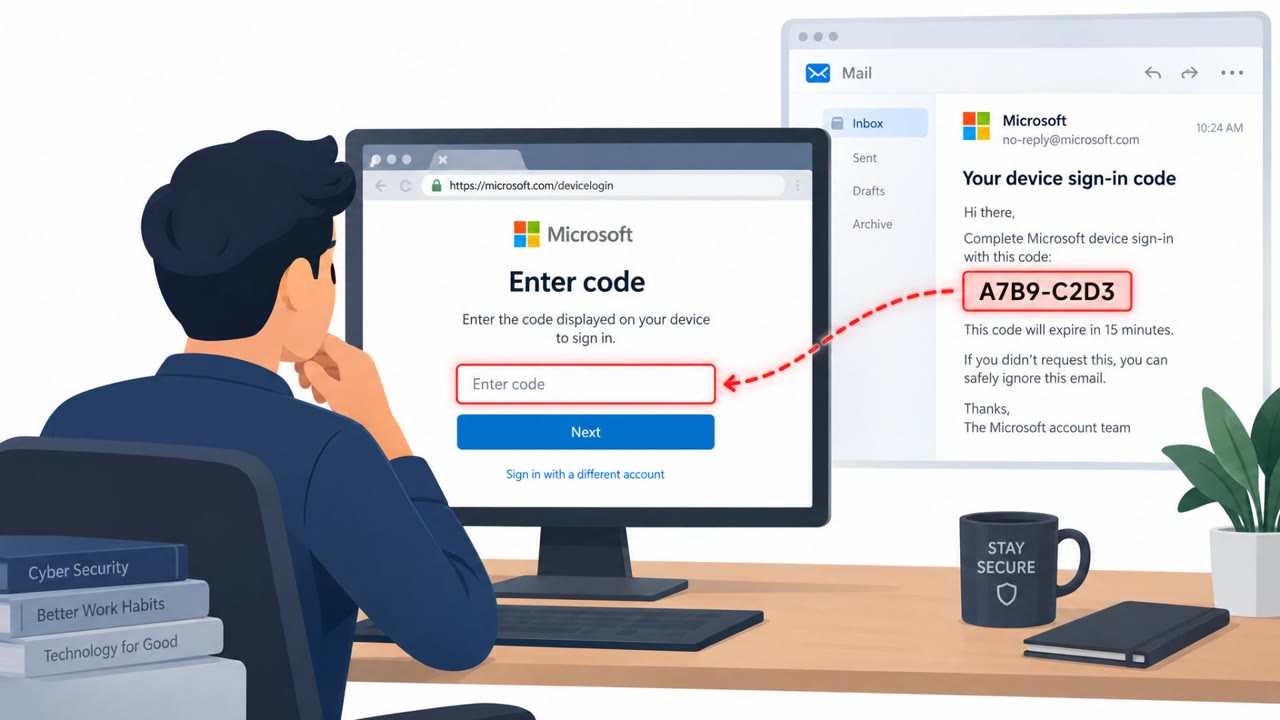
EvilTokens Uses Device Codes to Bypass MFA

EvilTokens Uses Device Codes to Bypass MFA

Microsoft reports that the EvilTokens phishing-as-a-service platform helped criminals compromise thousands of organizations by tricking users into completing a legitimate Microsoft “device code” login. The lure drives victims to enter a short code at microsoft.com/devicelogin, which unknowingly…

September 22, 2026
SideCopy Phishes Indian Universities With Fake Docs

SideCopy Phishes Indian Universities With Fake Docs

Pakistan-linked APT group SideCopy expanded from targeting Indian government entities to targeting Indian academic institutions using spear-phishing. The emails deliver a weaponized ZIP containing a fake “document” shortcut that launches mshta.exe to pull down and run malware, ultimately installing…

September 22, 2026
Fake Cloudflare Check Tricks Users Into Running PowerShell

Fake Cloudflare Check Tricks Users Into Running PowerShell

Researchers observed real-world infections where compromised WordPress sites showed a fake “Cloudflare Turnstile” verification and instructed visitors to press Win+R and run a PowerShell command. The attacker’s page guides victims step-by-step (and reports progress back to the operator) to execute…

September 21, 2026
Fake Cops Threaten Arrest to Force Payments

Fake Cops Threaten Arrest to Force Payments

The FBI warns about phone scams where callers impersonate police or federal agents and threaten arrest unless the victim pays immediately. The scams use pressure tactics (keeping victims on the phone, urging secrecy) and push hard-to-trace payments like prepaid cards, crypto, wire transfers, or…

September 21, 2026
FBI: Fake Cops Swindle $1.6B via Threat Calls

FBI: Fake Cops Swindle $1.6B via Threat Calls

The FBI says scammers posing as law enforcement or government officials stole over $1.6B since January 2025, mainly by calling victims and threatening arrest, fines, or legal trouble unless they pay. Variants include jury-duty threats, targeted calls to medical professionals about license issues,…

September 18, 2026
Fake ChatGPT Invoice Steals Login Credentials

Fake ChatGPT Invoice Steals Login Credentials

Cofense observed a real phishing email that impersonates OpenAI/ChatGPT billing to trick users into “updating” payment details. The email uses the real ChatGPT logo, urgency (“48 hours”), and a prominent button to drive clicks to a lookalike ChatGPT login page. Any credentials entered are harvested…

September 17, 2026
AI “Agents” Flood Inboxes With Spam Pitches

AI “Agents” Flood Inboxes With Spam Pitches

The article describes real-world examples of unsolicited emails that claim to be sent by “AI agents,” pitching services, interviews, coverage, and paid work. It includes specific subject lines and message excerpts that show a repeatable workflow: automated outreach that tries to prompt recipients…

September 15, 2026
Fake Downloads and Extensions Steal Sessions Fast

Fake Downloads and Extensions Steal Sessions Fast

The article highlights real, ongoing campaigns where attackers trick people into installing malware via fake software-download websites and a disguised browser extension. These lures are used to steal credentials, browser cookies, and authenticated sessions, letting attackers take over accounts…

September 11, 2026
Claude Linked to Real Phishing and Credential Theft

Claude Linked to Real Phishing and Credential Theft

Anthropic reports multiple real-world threat groups used Claude to support cyber operations, including credential harvesting and data theft across many victims. The report includes specific, simulation-ready lures such as a fake ESET NOD32 login portal that sends stolen passwords to Telegram and a…

September 11, 2026
One-Click Sogou Link Trick Dropped GRAYRABBIT

One-Click Sogou Link Trick Dropped GRAYRABBIT

Researchers reported a real intrusion where a China-linked group used a crafted link to exploit Sogou Input Method on Windows and install the GRAYRABBIT backdoor. Victims were lured into opening a special link (potentially via email or chat), which redirected Sogou’s built-in browser to an…

September 11, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo