Recent Financial Services Cyber Attacks

Page 6 of 13
Manic Malware Steals PINs With Fake Lock Prompts

Manic Malware Steals PINs With Fake Lock Prompts

Researchers report a real Android malware operation (“Manic”) active since at least February 2026 that blends banking fraud with spyware-style surveillance. It can trick users into revealing their device PIN/pattern via a fake lock prompt and silently capture banking PIN taps, then exfiltrate…

August 20, 2026
Wall Street Hit by Help Desk Impersonation Calls

Wall Street Hit by Help Desk Impersonation Calls

A real campaign of voice-phishing (vishing) calls targeted major hedge funds and private equity firms by impersonating internal IT/help desk staff. Victims were pressured into completing “routine” security steps and were sent to fake login pages that captured usernames, passwords, and MFA codes in…

August 20, 2026
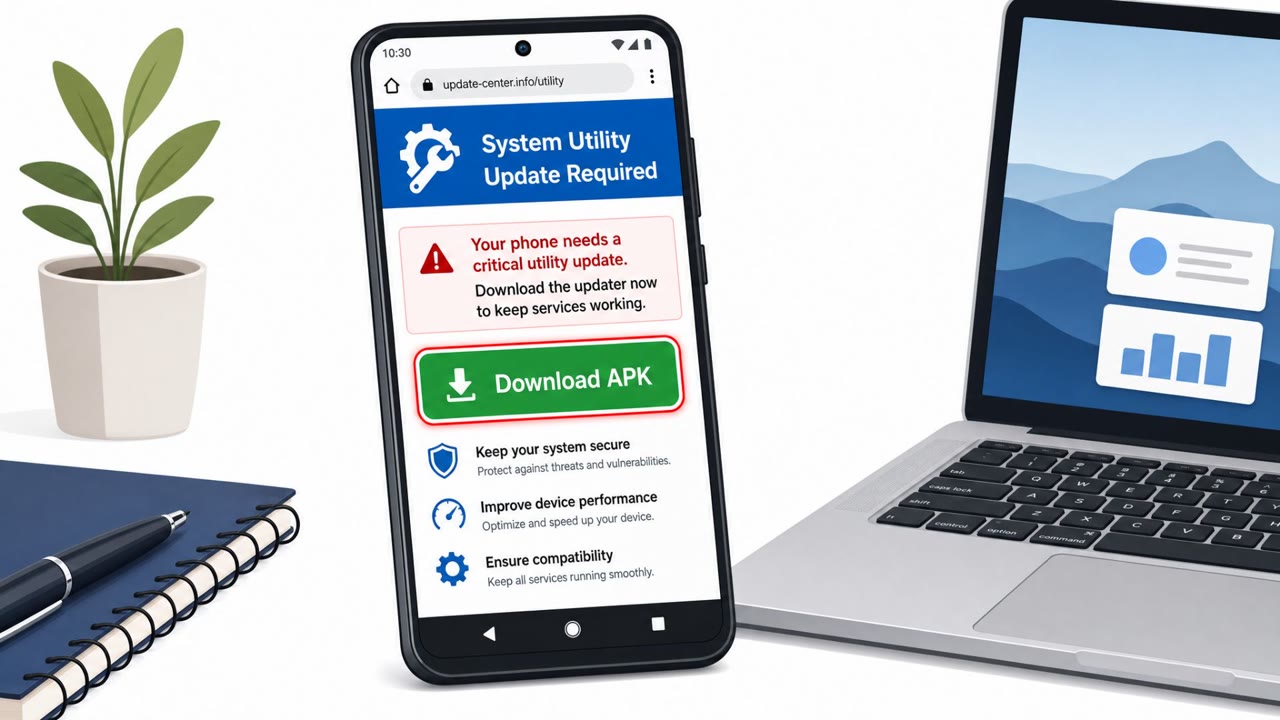
Manic Android Spyware Uses Fake Utility Apps

Manic Android Spyware Uses Fake Utility Apps

A new Android malware family called “Manic” is being used in real campaigns targeting banking, government identity, and messaging apps, especially in Ukraine and parts of Europe. It spreads through phishing sites and “dropper” apps disguised as legitimate utilities (including a booking-app lure),…

August 20, 2026
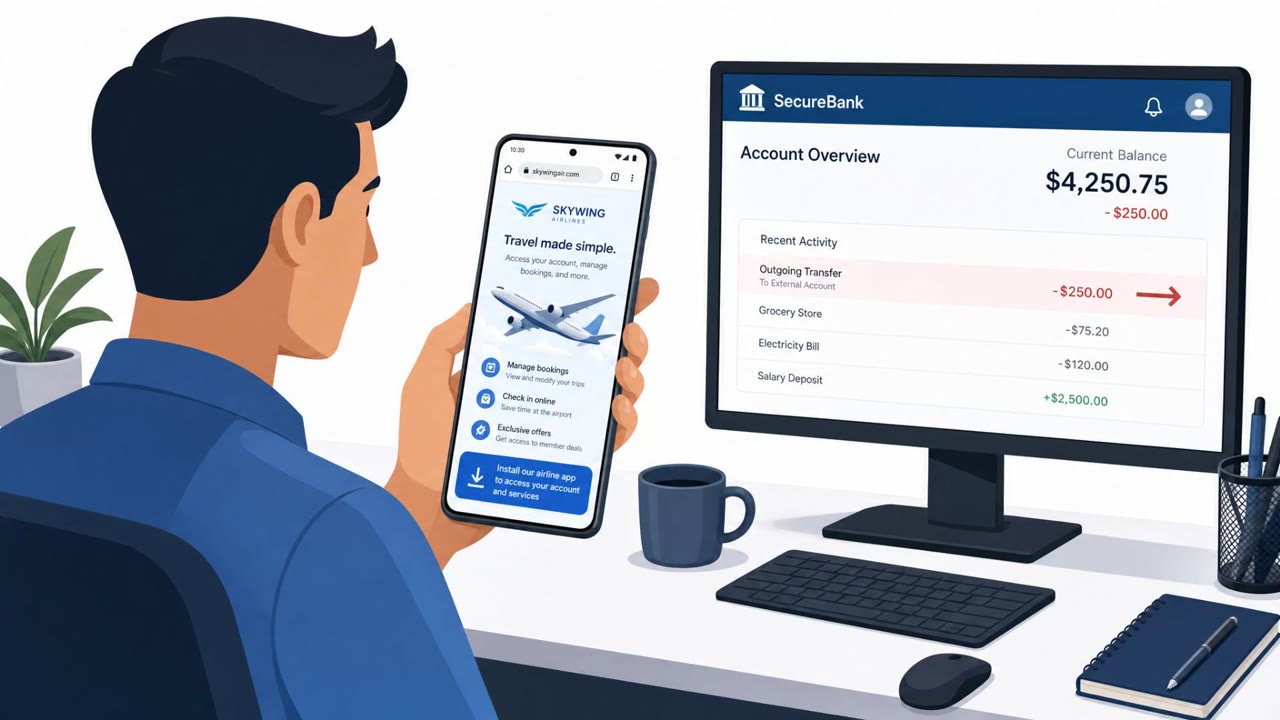
Fake Airline Apps Push Android Banking Fraud

Fake Airline Apps Push Android Banking Fraud

Researchers report two Android banking malware families (ToxicPanda 2.0 and GoldDigger) that rely on tricking people into installing malicious apps and granting powerful permissions. GoldDigger campaigns impersonate airlines and shopping retailers and then abuse Android Accessibility to take over…

August 20, 2026
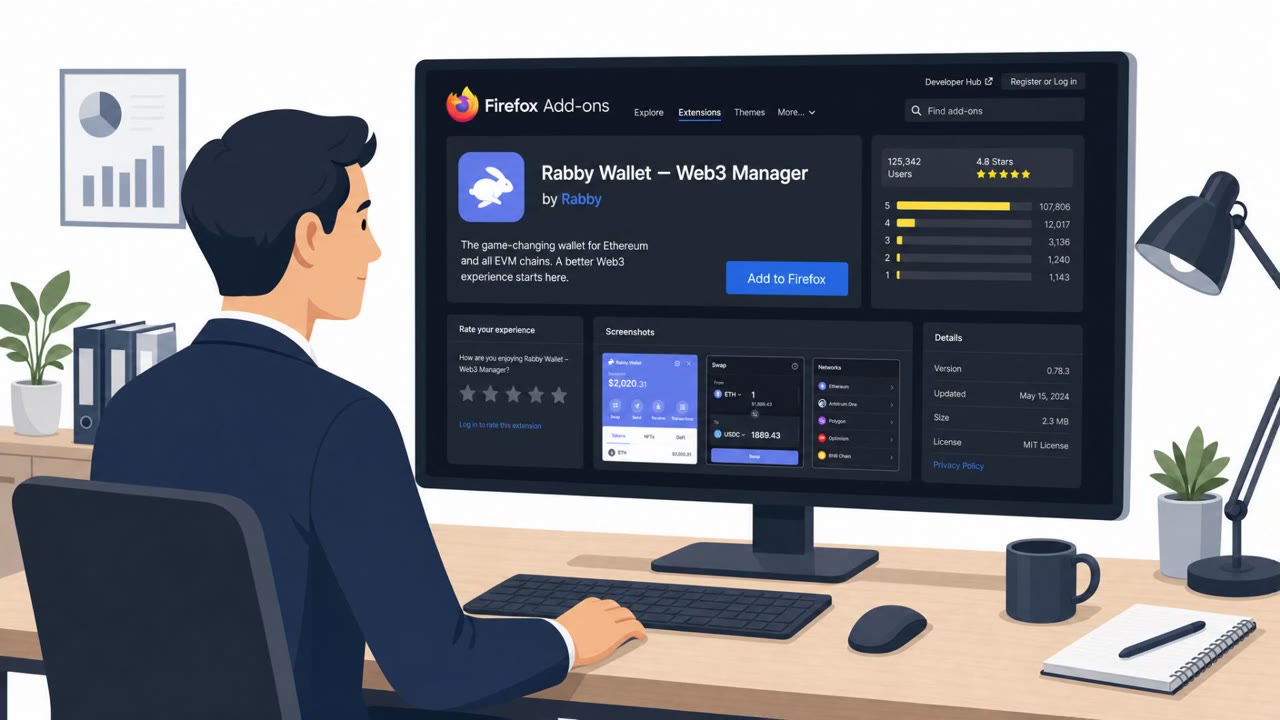
Fake Firefox Web3 Extensions Steal Wallet Secrets

Fake Firefox Web3 Extensions Steal Wallet Secrets

Researchers found 40 malicious Firefox extensions pretending to be popular Web3 wallet products (like OKX, Rabby Wallet, and TronLink) to steal crypto wallet secrets. The extensions trick users into installing them, then capture recovery phrases/private keys and send them to attacker-controlled…

August 20, 2026
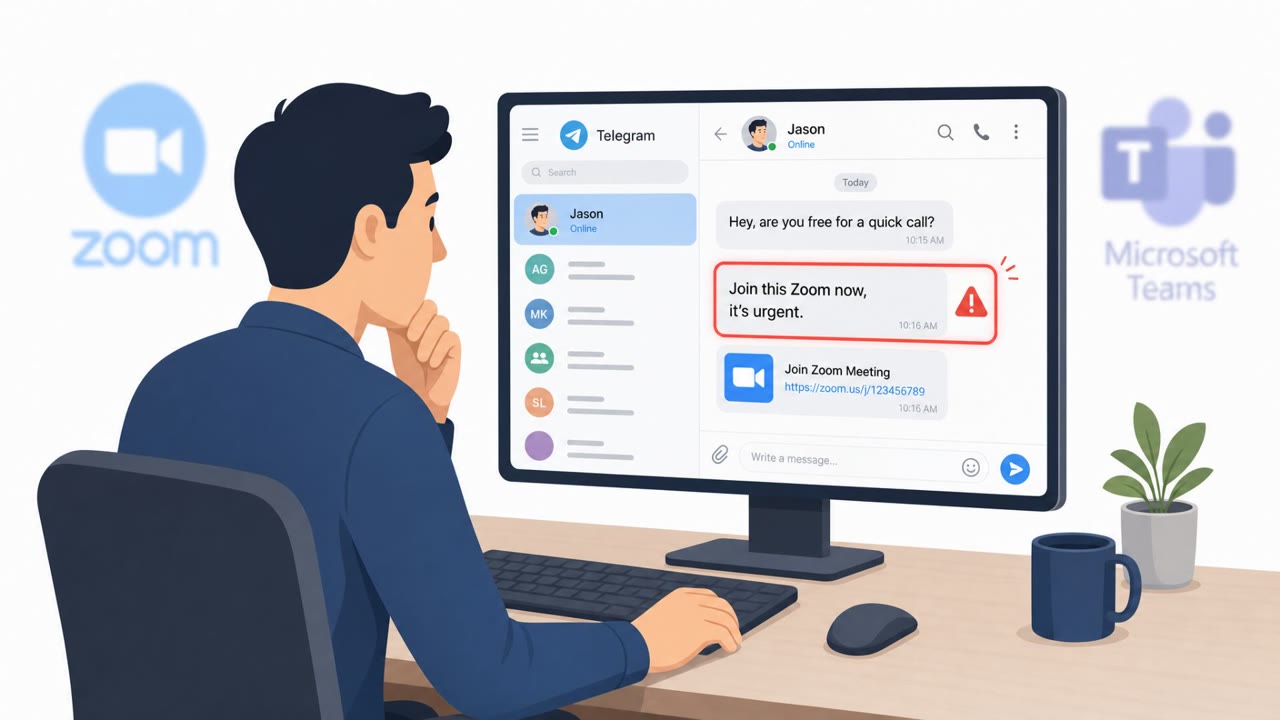
APT Groups Lure Targets Into Fake Zoom/Teams Meets

APT Groups Lure Targets Into Fake Zoom/Teams Meets

This threat trend report describes multiple real-world APT campaigns where attackers rely on social engineering and trusted services (Zoom/Teams, Telegram, webmail, GitHub) to steal credentials and access cloud accounts. Notable examples include fake meeting lures to deliver malware, and abuse of…

August 20, 2026
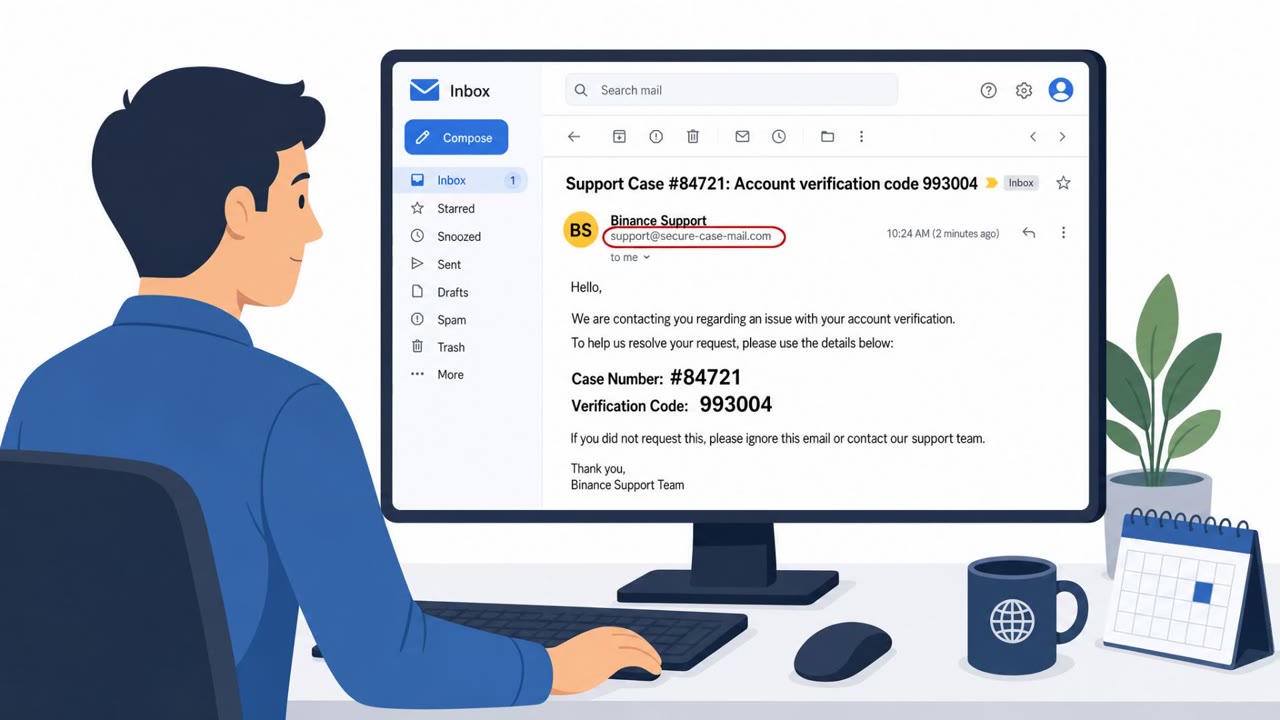
AI-Aided Crypto Scam Used Phishing + Vishing Combo

AI-Aided Crypto Scam Used Phishing + Vishing Combo

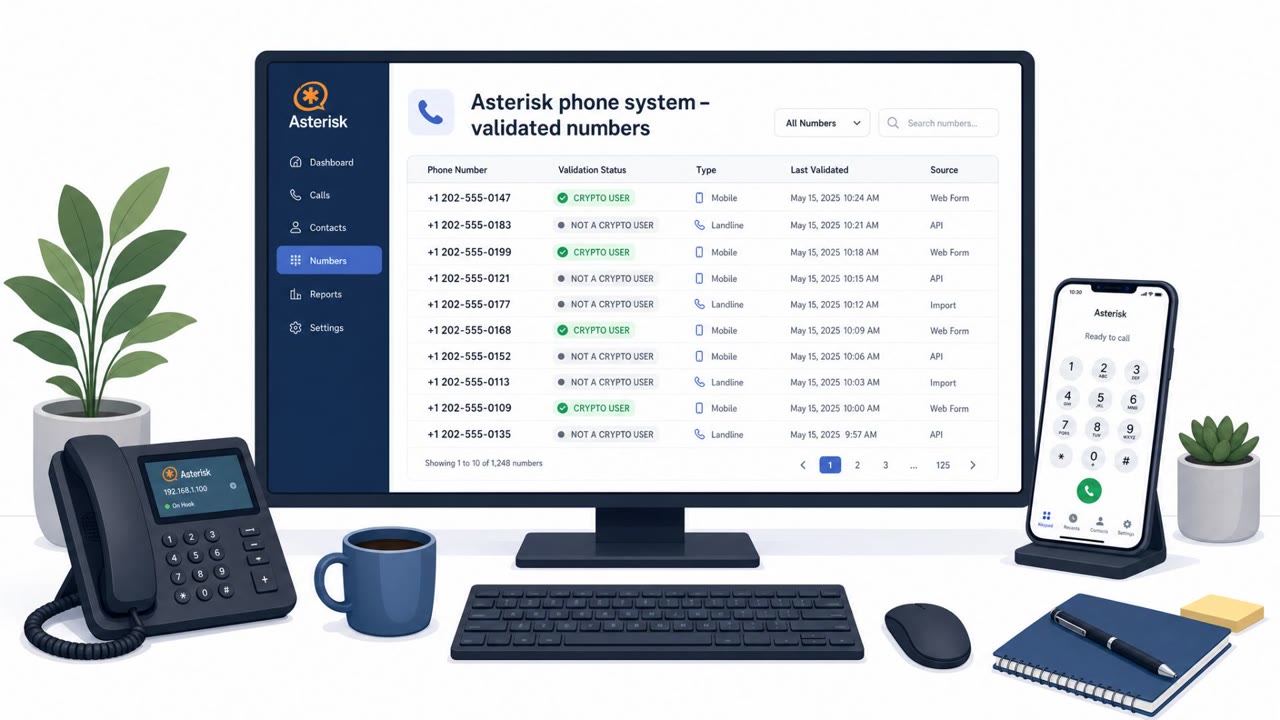
Researchers found a crypto fraud operation that used AI-assisted tooling to sift and verify over 100,000 phone numbers, then target confirmed crypto users. The campaign used a one-two approach: phishing messages that included a case/verification code, followed by phone calls that referenced those…

August 19, 2026
Fake Crypto “AML Checkers” Drain Wallets

Fake Crypto “AML Checkers” Drain Wallets

Scammers are running professional-looking “AML checker” websites that pretend to screen crypto wallets for suspicious activity, but are designed to trick people into connecting their wallet and approving a malicious transaction. Many impersonate a legitimate service (AMLBot) and use fake progress…

August 19, 2026
ClickFix Tricks Mac Users Into Running Stealer

ClickFix Tricks Mac Users Into Running Stealer

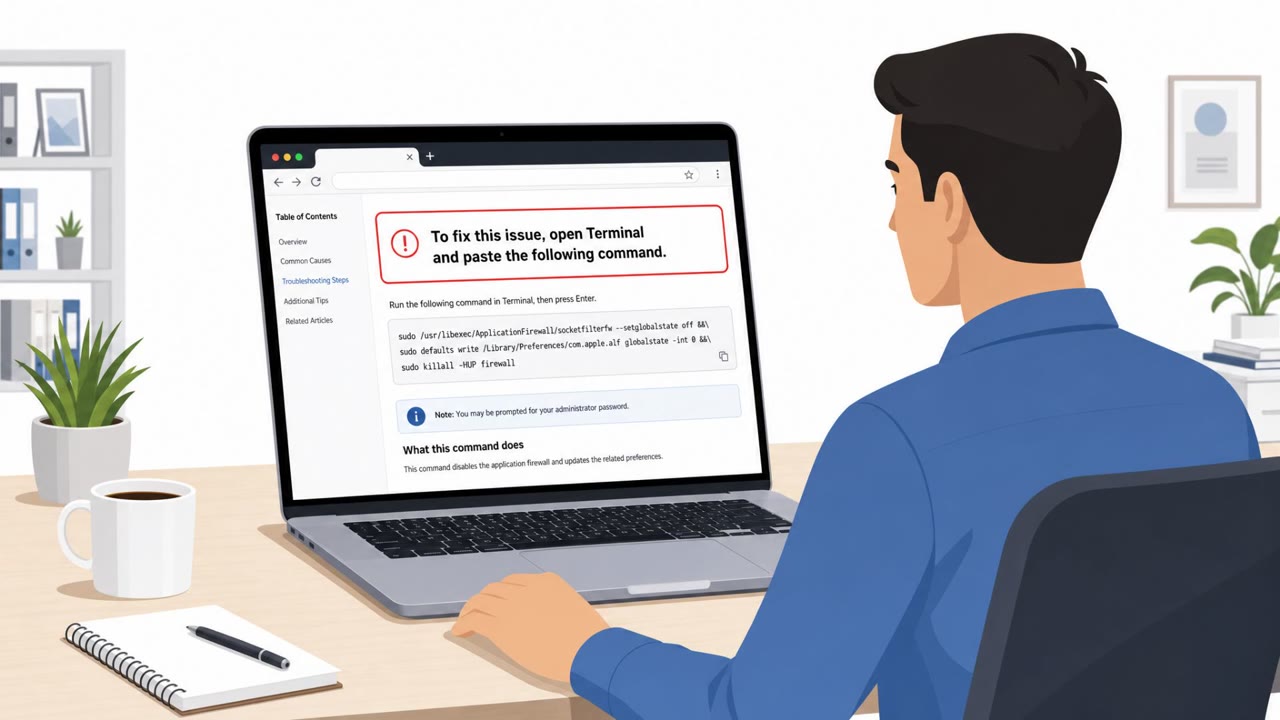
Microsoft describes a real macOS data-stealing campaign (MacSync Stealer) that relies on social engineering rather than software exploits. Victims are tricked into pasting/running commands in Terminal, which downloads the payload and ultimately steals passwords, keys, and wallet data, then uploads…

August 19, 2026
Wrong-Number Texts That Turn Into Scams

Wrong-Number Texts That Turn Into Scams

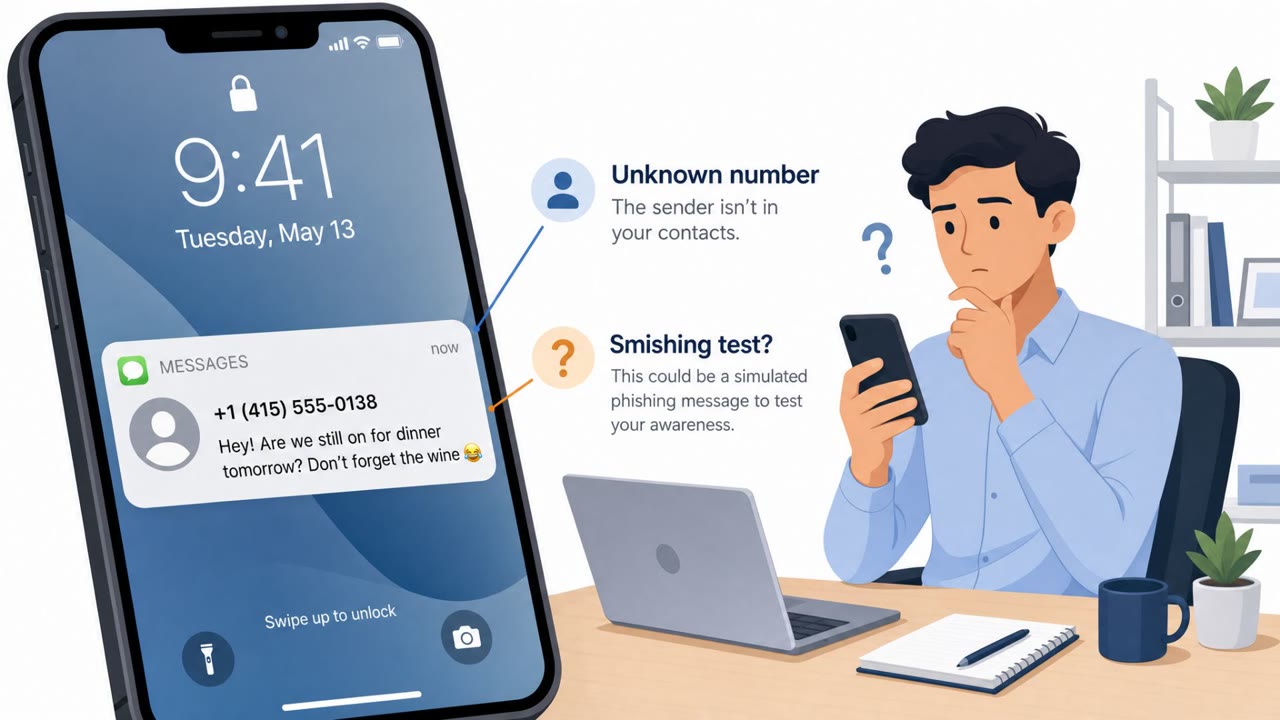
The article describes how “wrong-number” SMS messages are used as a first-step social engineering test to identify people who will engage with strangers. If the target replies, scammers may either build a long relationship that leads to fake investment fraud (“pig butchering”) or recycle the…

August 19, 2026
“Ransom Busters” Emails Victims for $60K “Help”

“Ransom Busters” Emails Victims for $60K “Help”

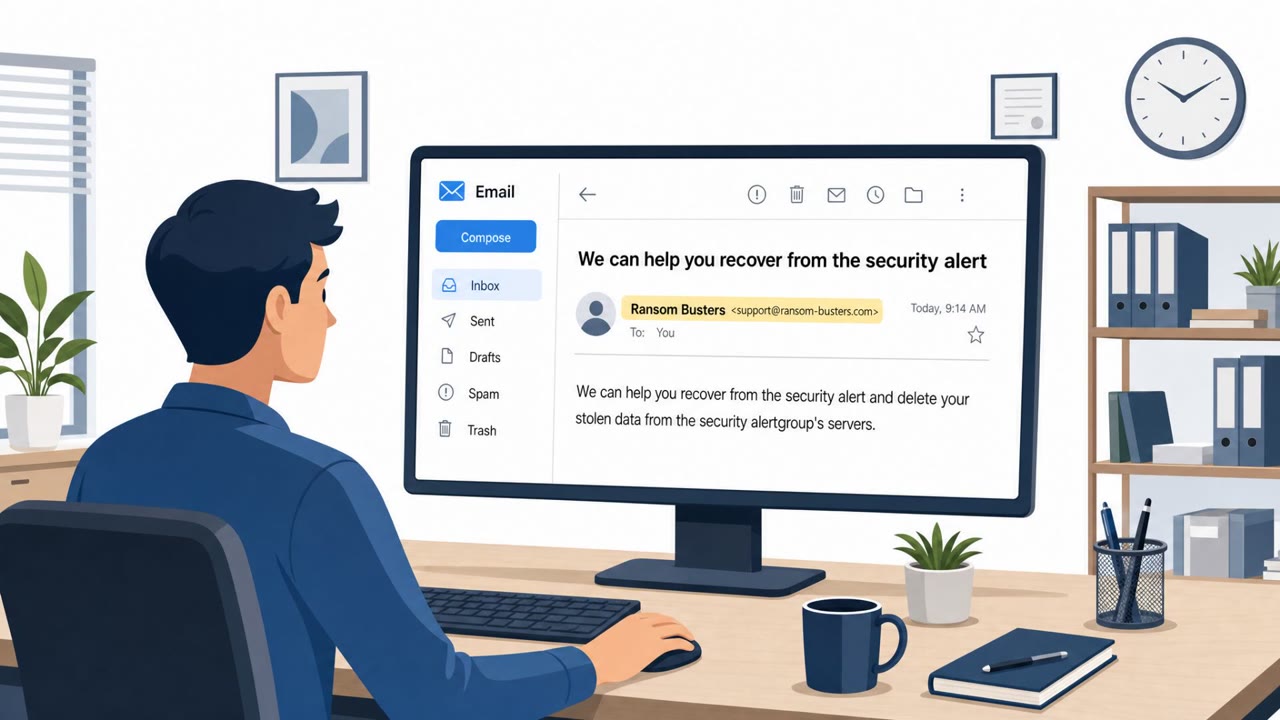
A criminal actor calling itself “Ransom Busters” is emailing organizations that recently suffered ransomware incidents, claiming it hacked ransomware groups’ servers and can delete the victim’s stolen data for a $20,000–$60,000 fee. The messages ask to speak with the CEO or IT leadership and…

August 18, 2026
One-Click Copilot Link Triggers Data Exfil

One-Click Copilot Link Triggers Data Exfil

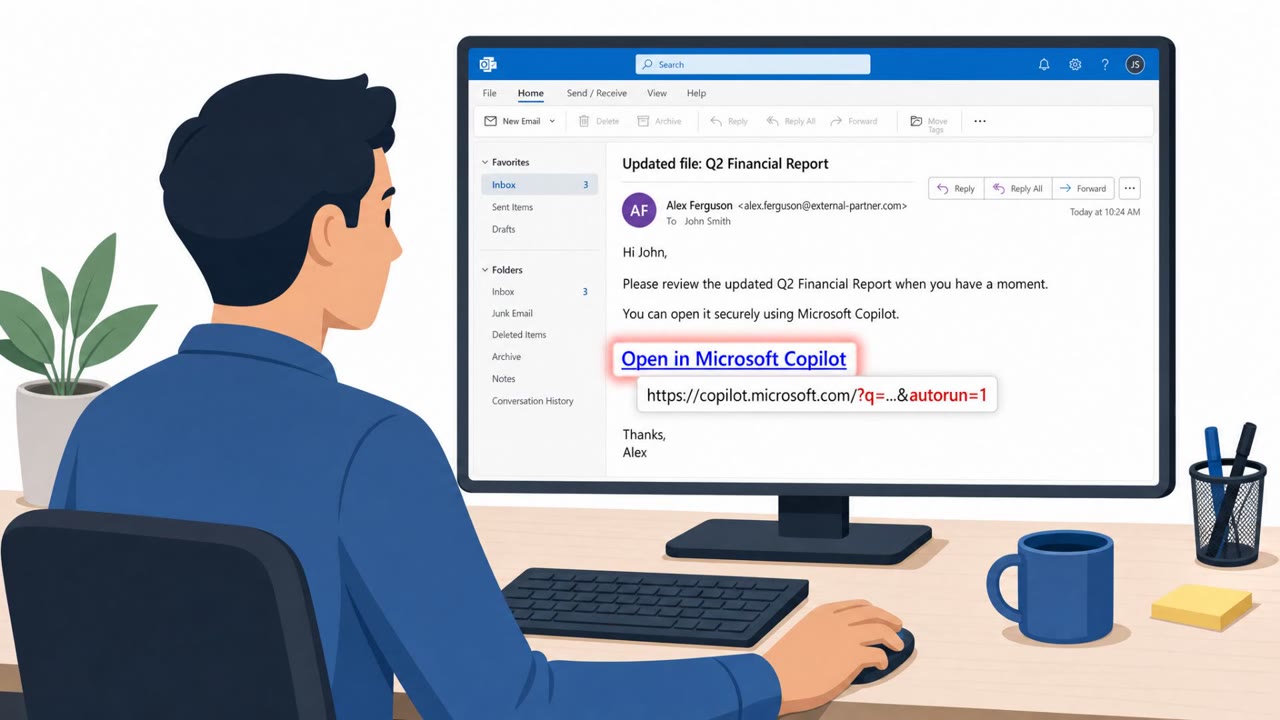
Researchers showed how an attacker could trick Microsoft Copilot into running a malicious prompt automatically just by getting a user to click a specially crafted link. The prompt can then make Copilot search connected accounts (like email and cloud storage) and send information to an external…

August 18, 2026
Fraud Ring Targets Crypto Users via Phone + Phish

Fraud Ring Targets Crypto Users via Phone + Phish

Researchers described a real fraud operation that first verified which phone numbers were tied to cryptocurrency exchange accounts, then targeted confirmed owners. The attackers used phishing emails, vishing calls, and fake wallet apps while impersonating popular hardware/software wallet brands,…

August 18, 2026
Fake Transaction Receipt Emails Drop Remote Access Tool

Fake Transaction Receipt Emails Drop Remote Access Tool

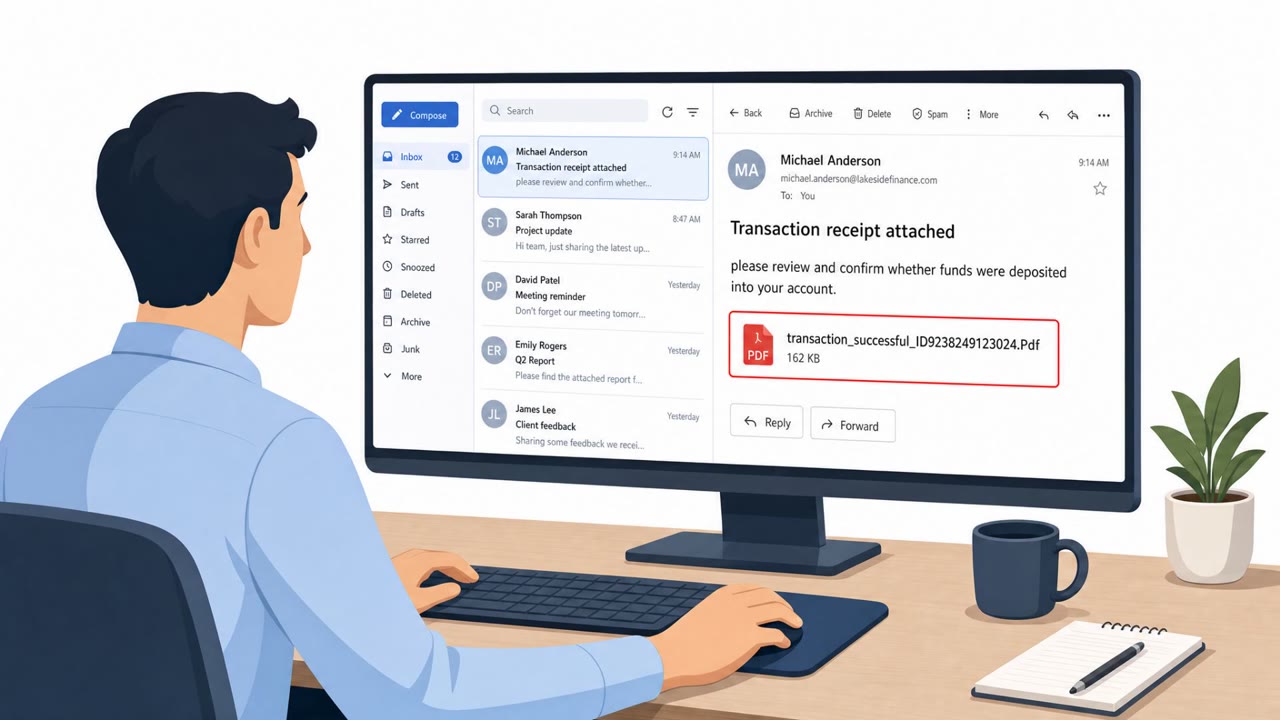
Researchers observed real phishing emails posing as transaction receipts to trick people into opening a PDF attachment. The PDF claims an “Adobe Flash Player update is required,” leading victims to download and run a script that silently installs ScreenConnect for persistent remote access.

August 18, 2026
BlackFile Vishing Poses as IT Support to Extort Firms

BlackFile Vishing Poses as IT Support to Extort Firms

Researchers say the BlackFile extortion group is actively targeting large financial and other organizations using voice-phishing calls where attackers impersonate IT support to get initial access. Victims are then pressured with multimillion-dollar extortion demands and, in some cases, escalations…

August 17, 2026
SafePal Data Exposure Sparks Targeted Phishing Risk

SafePal Data Exposure Sparks Targeted Phishing Risk

SafePal disclosed that nearly 40,000 customers had personal and order information exposed due to an authorization flaw in an order-tracking plug-in. While wallet secrets were not exposed, SafePal warned that criminals can use the leaked order details to run highly convincing scams (fake support,…

August 17, 2026
Crypto Scam Used Email + Vishing + Fake Wallet Apps

Crypto Scam Used Email + Vishing + Fake Wallet Apps

Rapid7 uncovered an active cryptocurrency fraud operation that combined phishing emails, follow-up phone calls, and counterfeit wallet apps to trick victims into handing over wallet recovery (seed) phrases. The attackers validated and enriched phone-number leads first, then used matching “support…

August 17, 2026
WindRelay Scam: Tap Your Card, Lose Your Money

WindRelay Scam: Tap Your Card, Lose Your Money

Researchers say criminals are using a two-part Android malware setup (SpyNote + WindRelay) to trick victims into turning their own phones into NFC “relays” for contactless payment fraud. Victims are lured via phishing/smishing/vishing to install a malicious app, then persuaded on a live call to tap…

August 17, 2026
SafePal Leak Fuels Phishing by Fake “Support”

SafePal Leak Fuels Phishing by Fake “Support”

SafePal says an order-tracking plug-in flaw exposed order data for 39,798 customers, including names, contact details, shipping addresses, and purchase information. A customer reported receiving a suspicious email, letter, and phone call from someone pretending to be SafePal and urging them to…

August 17, 2026
Vishing Console + Fake CCleaner Trap Users

Vishing Console + Fake CCleaner Trap Users

This bulletin highlights multiple real-world threats, including voice-phishing (vishing) operations that industrialize account takeovers and a fake CCleaner download site that installs spyware. The items provide concrete, repeatable lures (a vishing-driven takeover workflow and a lookalike software…

August 17, 2026
Try Mirage

Mirage simulates attacks like these against your own team, live and safely, so you can measure how your people actually respond.

Get a demo